Threat detection for security teams too small to staff a night shift.
Wardell reads your cloud, identity and endpoint logs, groups related alerts into one case, and pages a Wardell analyst when something needs a human at 3 am.

Reads the logs you already have, with read-only access

AWS

Okta
Microsoft 365
Google Workspace

GitHub

Cloudflare

Slack

1Password
Three jobs a small team does by hand today, and what Wardell does instead.
Cases, not a wall of alerts
Wardell groups alerts that share a user, a host or an app into one case with a timeline. A phishing click, an OAuth consent and three inbox rules read as one story. Known-good noise closes itself and stays searchable.

Detections you can read and change
Every rule is plain YAML you can open, test against the last 30 days and edit. Start with 312 managed detections, then write your own for the systems only you run.

A person on call when your team is not
From 6 pm to 8 am and all weekend, a Wardell analyst takes the page, acknowledges in under five minutes, contains what they can and writes up what they did before your team logs in.

The coverage map lines every connected source up against the MITRE ATT&CK matrix, so gaps show up before an auditor or an attacker finds them.
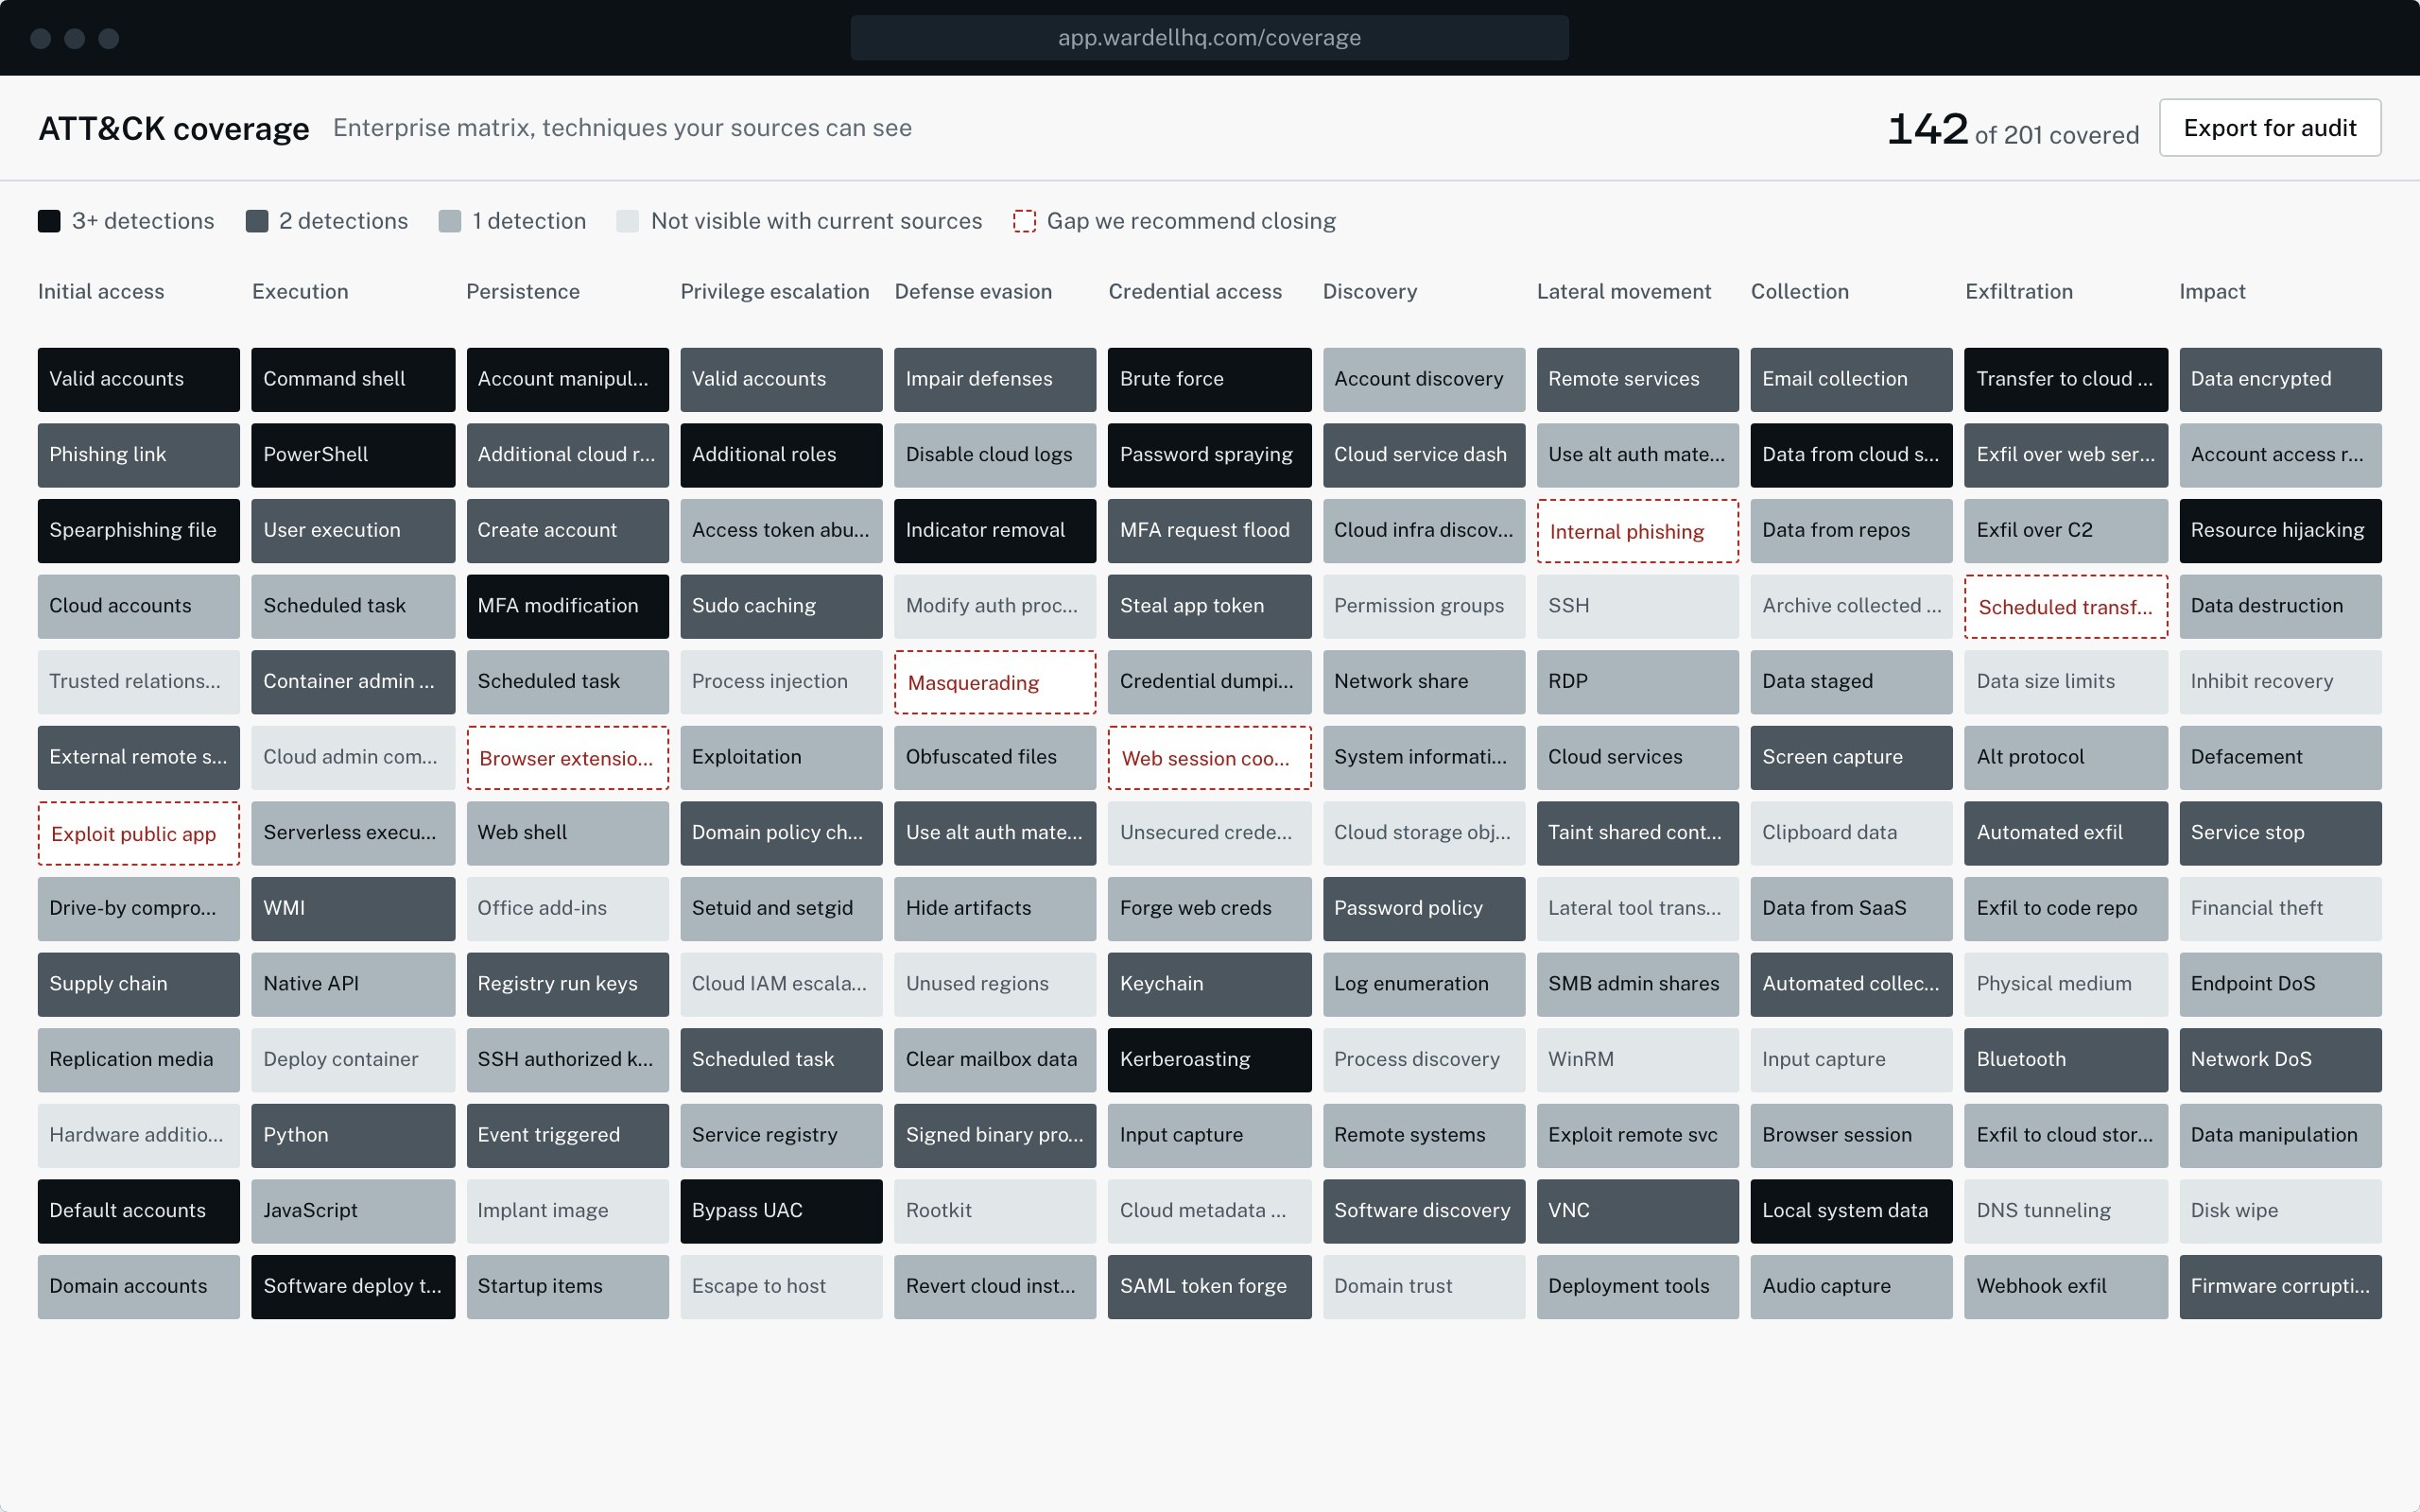
142 of 201 techniques
covered for a typical 400-person company on four sources
One source away
each gap names the log source that would close it
Audit-ready
exports as PDF and CSV evidence for SOC 2 and ISO 27001
No agents to install. Read-only keys, a week of tuning with an engineer, then night coverage switches on.
Connect with the keys and apps each vendor already offers. Every integration page lists exactly which events Wardell reads.




What changed for three customers in their first quarter.
96%
fewer alerts to read, six weeks in
“We used to start every Monday with 400 unread alerts. Now it is nine cases and a note from whoever was on call.”
Renata Oyelaran
Head of Security, Tallis Health, Nashville, TN
2m 38s
from the page to a person on the case
“The consent phishing case came in at 2:51 am. By the time I woke up it was contained and written up for our auditors.”
Marcus Heller
IT Director, Brightwater Freight, Columbus, OH
3 people
covering 1,400 employees around the clock
“We are three people. Wardell is the only reason we have a night shift at all, and it costs less than one hire.”
Leah Sandoval
Security Lead, Loomis Pay, Austin, TX
Add every log source you have. The bill does not move.
Team
For companies with 50 to 250 employees and one person on security.
- Up to 6 log sources
- Alerts grouped into cases, noise auto-closed
- 312 managed detections
- Analyst help on weekdays, 8 am to 6 pm
- 90 days of searchable history
Business
Most teams pick thisFor 250 to 2,000 employees. Nights and weekends are covered.
- Unlimited log sources
- A Wardell analyst on call nights and weekends
- 5-minute acknowledge target on every page
- Write your own detections in YAML
- One year of searchable history
- ATT&CK coverage and audit exports
Enterprise
Over 2,000 employees, or a regulated industry.
- Everything in Business
- US or EU data residency
- A named detection engineer
- SSO, SCIM and an audit log API
- Three years of history, 99.9% uptime SLA
Prices in USD. Log volume never changes the price. Every plan starts with a 48-hour threat review of one log source.
Questions security leads ask us first
Something else on your mind? Our team answers within one business day.
Send us one week of logs. We send back what we found.
Connect one source with a read-only key. Within 48 hours you get a written report of what Wardell would have caught. No contract, and you can disconnect at any time.