Detection, cases and a night shift for small security teams

Detection, cases and a night shift for small security teams

Wardell does three jobs: it reads your logs, it turns alerts into cases, and it puts a person on call when your team is not. Here is each part in detail.

One queue for every source

Okta, Microsoft 365, Google Workspace, AWS and your EDR land in one queue with severity, owner and age. Filters are saved per person, and anything unassigned for 30 minutes pings the channel.

The Wardell alert queue with severity, source, case, owner and age

Cases that tell the whole story

Alerts that share a user, a host, an app or an IP become one case with a single timeline. Evidence from every source sits on the case, with suggested next steps and one-click containment for Okta, Microsoft 365 and Google Workspace.

A Wardell case timeline with evidence and suggested next steps

Detections you can read, test and change

312 managed detections, each a plain YAML file mapped to ATT&CK. Run any rule against the last 30 days before you save it, and see exactly what it would have caught and what it would have paged.

The Wardell rule editor with a YAML detection and test results

A night shift without hiring one

From 6 pm to 8 am and all weekend, Wardell analysts take your pages. They acknowledge in under five minutes, contain what you have pre-approved, and leave a written hand-off for 8 am.

The Wardell on-call schedule and page log

Source health you can trust

Every source is checked every 60 seconds. When a source goes quiet or starts arriving late, you hear about it before it becomes a blind spot, and the delay shows on every case it affects.

The Wardell sources table with health, volume and last event

See which attacks your logs can catch, and which they cannot

See which attacks your logs can catch, and which they cannot

The coverage map lines every connected source up against the MITRE ATT&CK matrix. Each gap names the source that would close it.
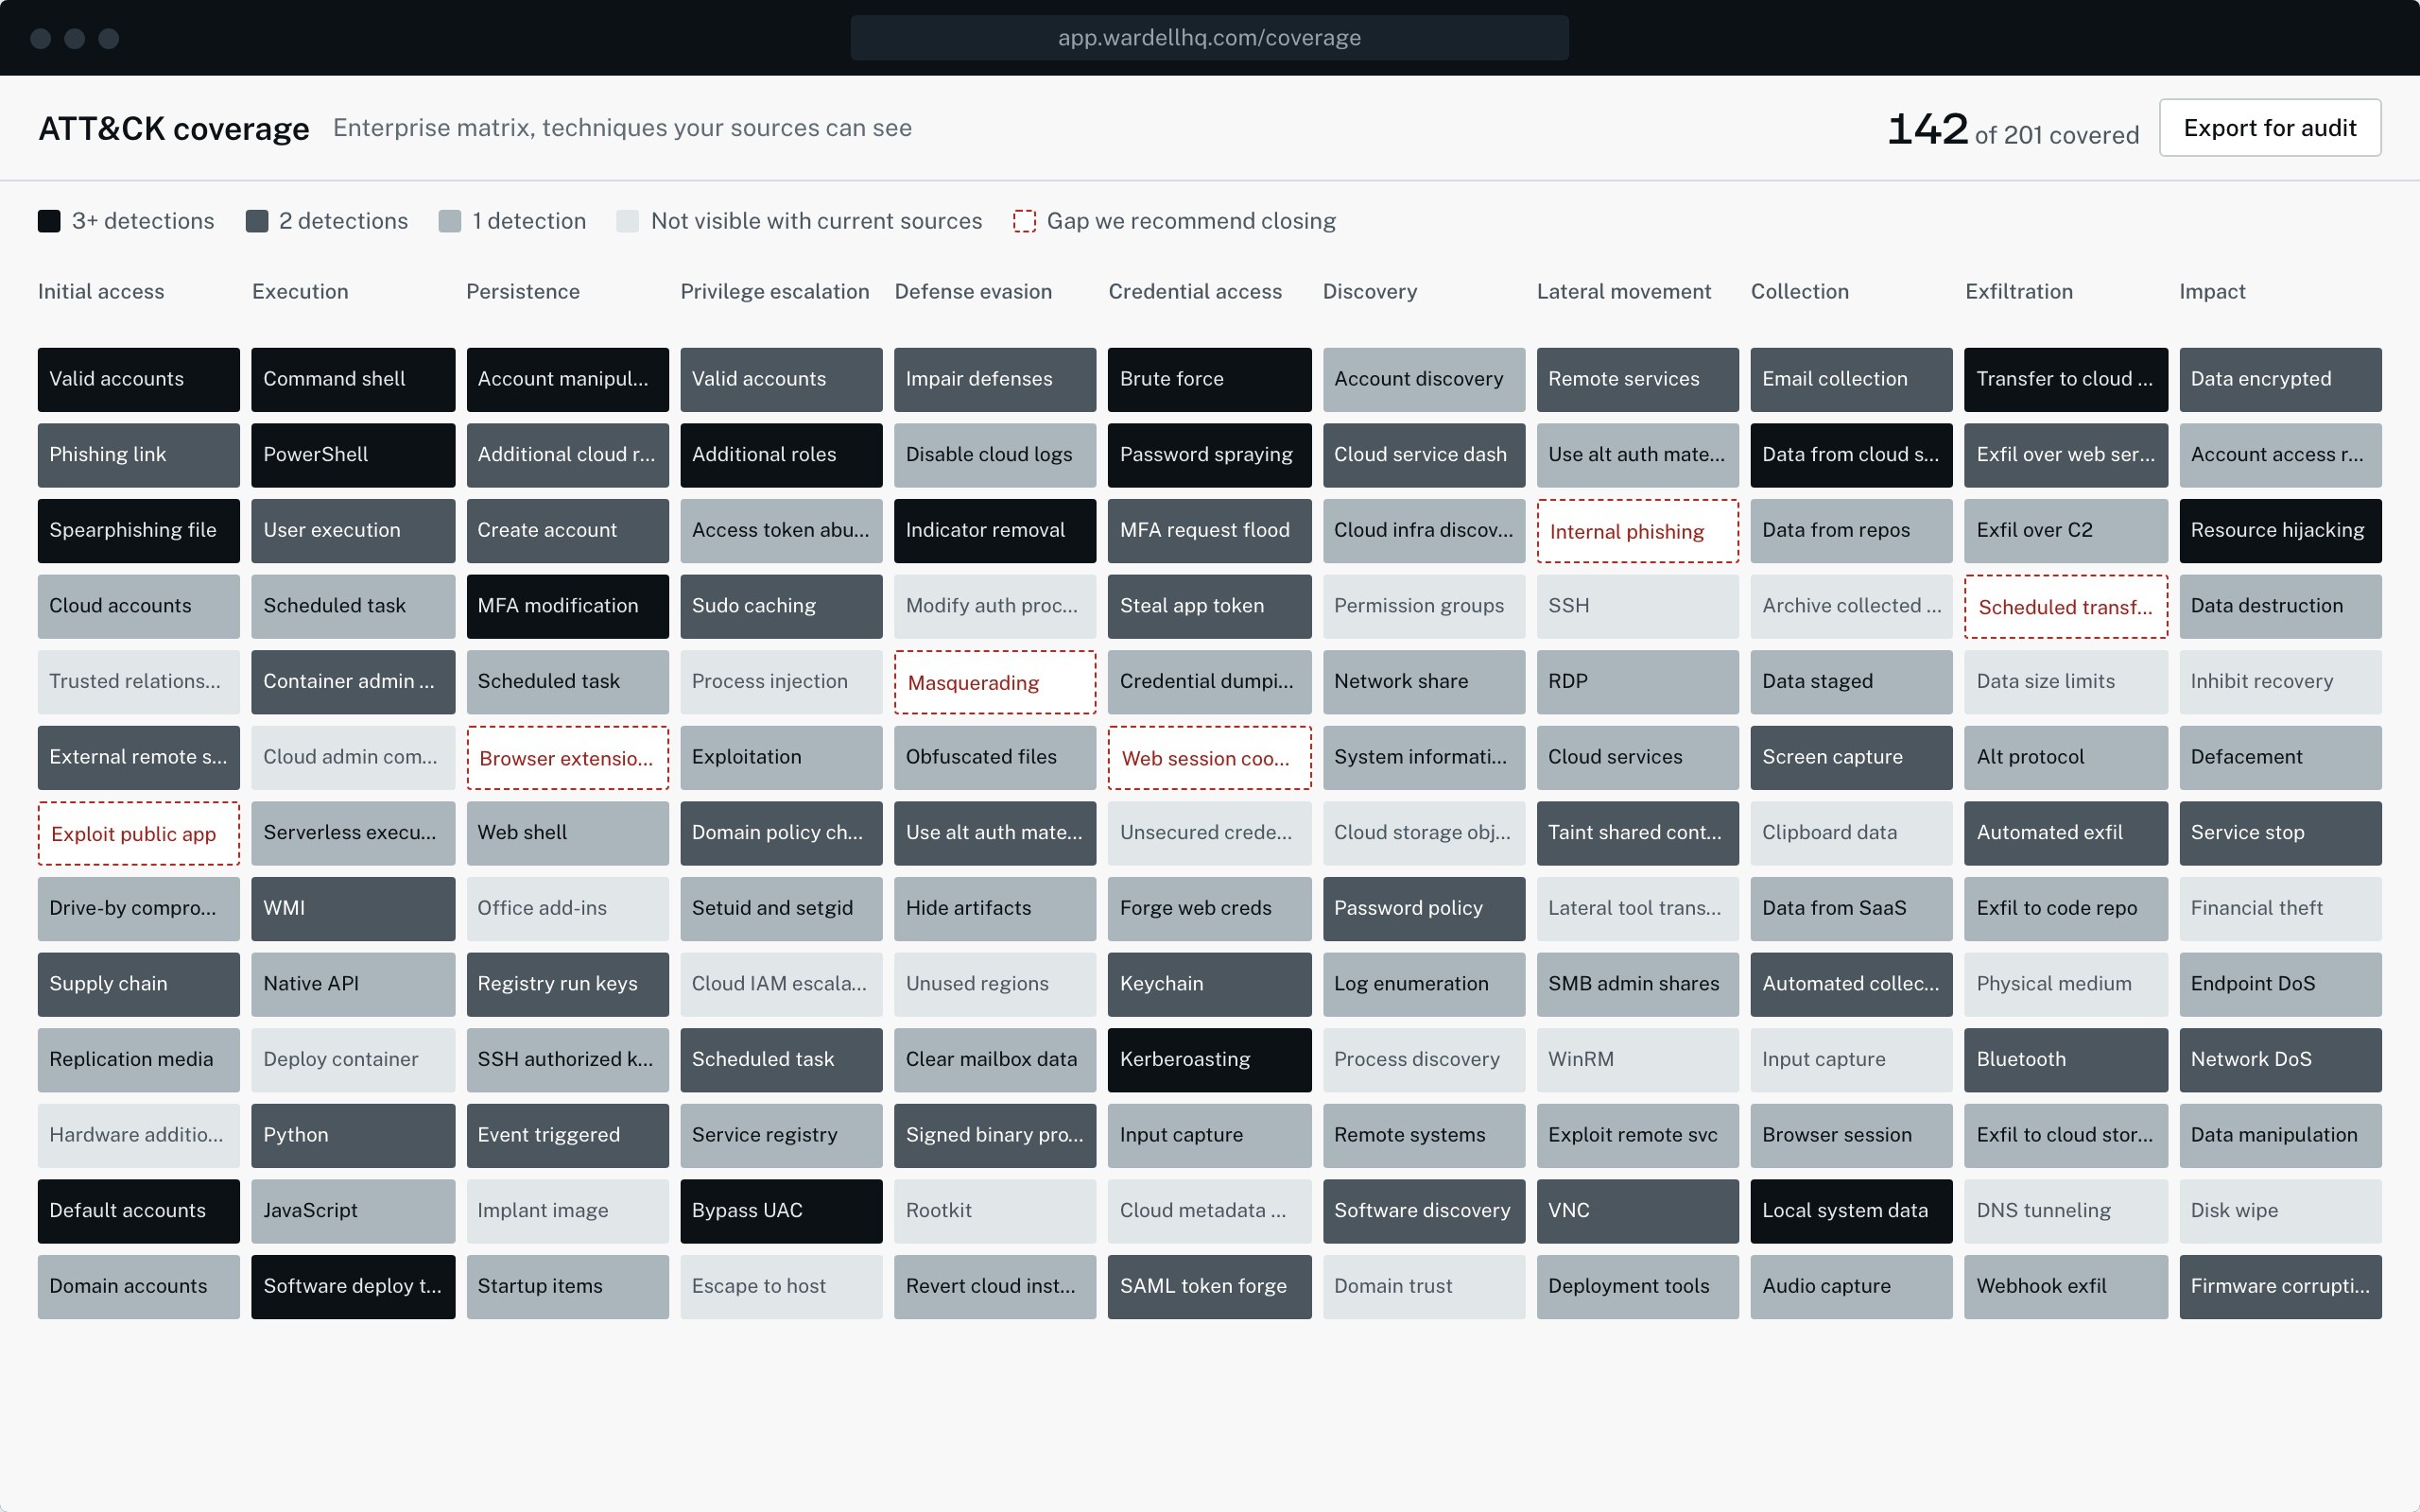
Wardell ATT&CK coverage matrix

The controls you will be asked about

The controls you will be asked about

Wardell holds your logs, so we hold ourselves to the same questions your auditors ask you.

SOC 2 Type II

SOC 2 Type II

Report available under NDA. Audited yearly by an independent firm.

Report available under NDA. Audited yearly by an independent firm.

Data residency

Data residency

US regions in Oregon or Virginia, or Frankfurt for EU teams.

US regions in Oregon or Virginia, or Frankfurt for EU teams.

Encryption

Encryption

TLS 1.3 in transit, AES-256 at rest with a key per customer.

TLS 1.3 in transit, AES-256 at rest with a key per customer.

Access

Access

SSO with SAML or OIDC, SCIM provisioning and role-based permissions.

SSO with SAML or OIDC, SCIM provisioning and role-based permissions.

Audit log

Audit log

Every action in Wardell is logged and available through an API.

Every action in Wardell is logged and available through an API.

Your data, your call

Your data, your call

Export everything at any time. Deletion completes within 30 days of a request.

Export everything at any time. Deletion completes within 30 days of a request.

Send us one week of logs. We send back what we found.

Connect one source with a read-only key. Within 48 hours you get a written report of what Wardell would have caught. No contract, and you can disconnect at any time.

Use this free template

Create a free website with Framer, the website builder loved by startups, designers and agencies.